Why can the intern see my salary?
A hidden admin screen does not prove your data is protected. Ask what ordinary employees can view, change, export and share before you sign off.
Read the articleA failed screen does not prove a failed payment. Before blaming the customer for clicking twice, ask what your checkout made safe.
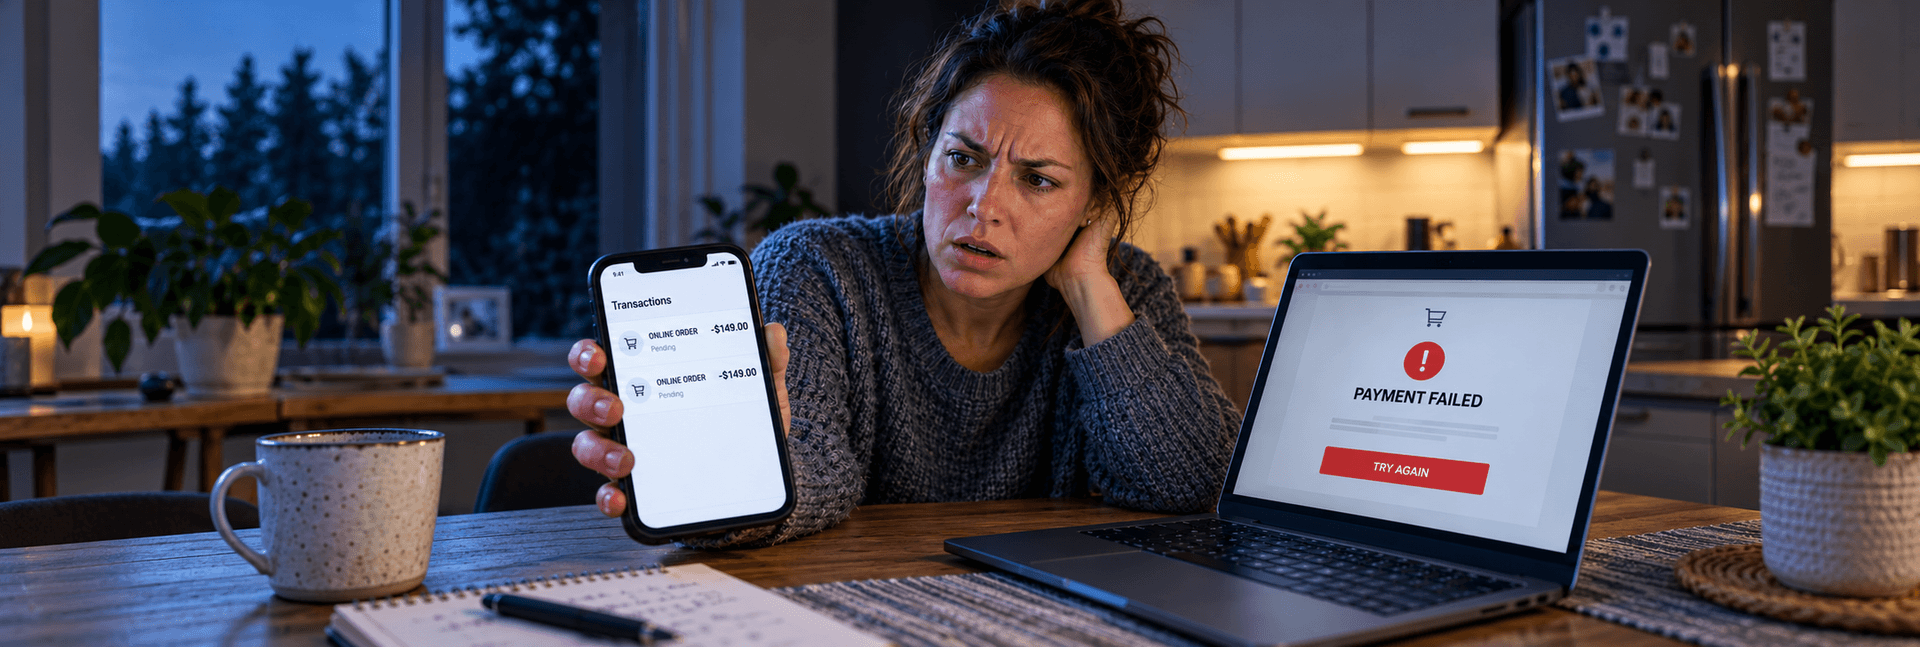
Now the customer has to decide whether pressing the button again will fix the order or charge them twice.
You paid to acquire this person. They chose the product, entered their details and agreed to the price. At the moment you ask them to trust you with money, your application hands them an error message and a guessing game.
Then somebody calls it user error because they clicked twice.
If your interface says “try again,” another attempt is a predictable response. The awkward question belongs to the business: what did you make safe before inviting that click?
Consider an illustrative checkout, not a reported client incident. A customer buys a $149 item. The payment service processes the request, but a connection drops before the application gets the response. The customer sees an error. A second attempt creates another payment instead of checking the first. Their phone now shows two entries, while the shop has no useful confirmation.
The cover depicts that invented situation. Two pending entries are not, by themselves, proof of two completed charges. An authorization can reserve funds before capture, and some banking interfaces make the distinction unclear. Stripe explains that separation in its authorization and capture guidance. Your support team needs to establish what actually happened.
The underlying ambiguity is real. Stripe’s error-handling documentation says a lost connection can leave the request outcome unknown. For retries of the same API v1 operation, preserve the idempotency key and parameters within its documented retry window. Changing the key can start another operation. An unresolved result needs reconciliation, not a fresh payment created on a guess.
You do not need to memorize the API to own a business. You do need your developer to explain how the application tells the difference between “declined,” “still processing” and “we haven’t confirmed the result.” Those situations need different next steps.
For an uncertain result, a more useful message might be: “We’re checking your payment. Please don’t pay again yet. Your reference is ABC123.” Give the person somewhere to check that reference and a way to reach support. Use that wording only if the system really is checking; an indefinite spinner with a comforting sentence is still an unresolved problem.
If payment is confirmed but the order is delayed, say so. If the payment definitely failed and another attempt is safe, offer that next step. Do not promise “you haven’t been charged” because the browser failed to load a confirmation page.
Decide who handles cases that remain uncertain. How will the team find them? What evidence will they use? What will they tell the customer, and when? A small business may use a straightforward review queue. A larger operation may need automated checks and escalation. Either way, an owner and a process beat hoping somebody complains.
A successful test purchase establishes that one successful path works. Before accepting the integration, ask the team to demonstrate interruptions in an authorized test environment with the provider’s test tools. Agree on the expected payment, order and customer-visible result before each case.
These are proposed acceptance checks, not claims that we ran them against your application. The relevant cases depend on your provider, payment methods and business rules. Ask for the records proving the result. A screenshot of a green check mark cannot show whether two orders were created behind it.
Follow one purchase through the whole system: the payment record, the local order, the stock reservation or access grant, and the confirmation the customer receives. Each step needs to refer to the same intended purchase. That makes a support investigation possible without asking the customer to assemble your transaction history.
Payment providers can notify your server independently of the customer’s browser. Stripe’s webhook documentation warns that events can be delivered more than once and are not guaranteed to arrive in order. It also requires checking their authenticity. Your integration has to handle those conditions; receiving a notification is not permission to repeat every business action.
A practical acceptance question is whether an interrupted job can resume without creating another shipment, booking or access grant. The answer lives in the application’s records and processing rules. Adding a webhook endpoint or disabling a button does not, on its own, prove the whole workflow is safe.
Keep enough information for support to find the purchase using a safe reference. They should be able to see the provider’s current payment state, the order state and the next recovery action. Do not ask customers to email full card details to help you debug a checkout.
They tried to pay. Having to wonder whether the money is gone, whether the order exists and whether another click will make it worse is a poor reward for that trust.
“The payment provider handles it” is an incomplete answer when your application owns the order and tells the customer what to do next. The provider’s documentation can help your team build the integration. It cannot choose your recovery process or write an honest status message for a state you never recorded.
At Rosecraft, we can review an existing payment flow, trace where its records disagree, and implement the agreed fixes. Bring the checkout steps and a redacted example of the confusing result. We can start with the system you already have.
If customers have to ask whether their payment worked, send us the flow. Ready to hear what needs fixing, even if the happy-path demo passed? Message Rosecraft. Your customer should not have to fund the investigation.

With your permission, Google Analytics helps us understand which pages people visit. Analytics cookies stay off until you accept. You can change this in Cookie settings.